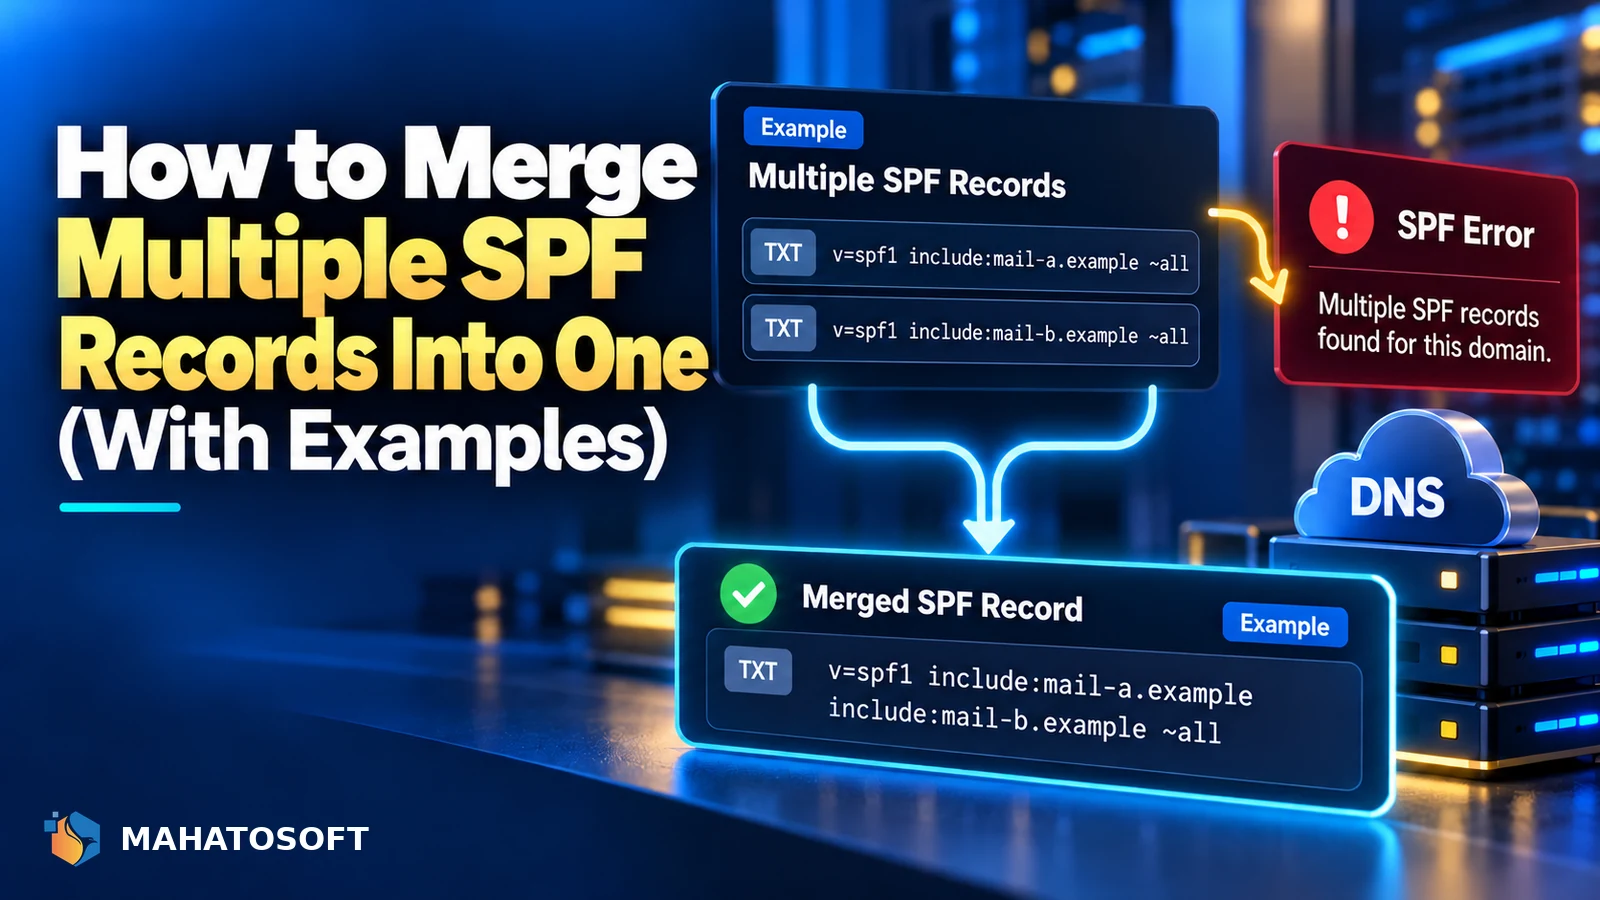
A domain can have only one SPF record, so multiple SPF records almost always mean SPF is failing for every email you send, not just the newest service you added. The fix is a five-minute DNS change once you know which records exist. This guide shows exactly how to merge multiple spf records into one that works.
SPF breaks silently in this case. There is no warning in your email client, no bounce message explaining it, just gradually worse deliverability as receiving servers see a rule violation and stop trusting your authentication.
Check first, before changing anything
Put your domain into our free SPF, DKIM and DMARC checker. It reads your live DNS and tells you immediately whether you have two SPF records, so you are not guessing.
Why a domain can only have one SPF record
SPF is published as a plain TXT record in DNS starting with v=spf1. The SPF standard (RFC 7208) is explicit: if a domain publishes more than one SPF-type TXT record, the result is a PermError, a permanent error, and most receiving mail servers treat that as a failure. Two records is worse for deliverability than having no SPF record at all, because at least no record just skips the check.
How multiple SPF records happen
This almost never happens on purpose. The usual story: a domain already has SPF set up for its main mail provider, such as Google Workspace or Microsoft 365. Then someone adds a newsletter tool, a helpdesk, or a CRM that sends email, and pastes that service’s suggested SPF record straight into DNS as a brand new TXT record instead of adding it to the existing one.
Each service’s setup instructions usually say “add this SPF record”, which is technically correct advice given in isolation, but wrong once you already have one.
Step 1: Find every SPF record on the domain
Check your DNS zone directly in your registrar or DNS host’s control panel, and look for every TXT record starting with v=spf1. You can also query it from a terminal:
dig TXT yourdomain.com +short
Or use an online tool such as MXToolbox’s SPF lookup, which will explicitly flag “Too many SPF records” if it finds more than one.
Step 2: Merge multiple spf records into one line
Take the include: or ip4:/ip6: mechanisms from every existing record and combine them into a single TXT record. For example, if you had these two separate records:
v=spf1 include:_spf.google.com ~all
v=spf1 include:servers.mcsv.net ~all
Merge them into one:
v=spf1 include:_spf.google.com include:servers.mcsv.net ~all
Keep only one all mechanism, at the very end, and keep whichever qualifier you had before (~all for softfail or -all for hardfail). Never include two.
Step 3: Delete the old records and publish the merged one
In your DNS panel, delete both original SPF TXT records and add the single merged line in their place. Do not leave the old ones “just in case”; a duplicate at this stage recreates the exact problem you are fixing.
| Field | Value |
|---|---|
| Type | TXT |
| Host/Name | @ (or your root domain, depending on the registrar’s convention) |
| Value | Your merged v=spf1 ... line |
| TTL | Default is fine, or lower it temporarily while testing |
Watch the 10-lookup limit while you merge
Each include: mechanism can trigger further DNS lookups of its own. RFC 7208 caps the total at 10; once you cross that, SPF returns a PermError again, the same failure mode as having two records. If merging pushes you over the limit, remove includes for services you no longer use, or replace less important ones with direct ip4: ranges where the provider publishes them. Our guide on SPF PermError: too many DNS lookups covers this in detail if you hit it.
Step 4: Verify the fix
Wait for DNS to propagate, usually within an hour, then re-check with our SPF checker or by sending a test email to a Gmail address and using Show original to confirm SPF now shows PASS. Also re-run the MXToolbox lookup to confirm only one record remains.
Preventing multiple SPF records in future
- Whenever a new service asks you to “add an SPF record”, check your DNS first to see if one already exists, and merge instead of adding a second.
- Keep a simple running note of every service included in your SPF record, so nobody accidentally duplicates or removes one during a later change.
- If several people or departments manage DNS, agree that SPF changes go through one person or a documented process.
Check DKIM and DMARC while you are in DNS
Since you are already editing DNS to merge multiple SPF records, it is worth confirming DKIM and DMARC are healthy at the same time rather than coming back to it later. DKIM needs a separate TXT record per selector, and it also needs to be switched on in your mail provider’s admin console, not just published in DNS. DMARC needs exactly one TXT record at _dmarc.yourdomain.com, and the same “only one record” rule applies there too, so check you have not accidentally duplicated that one as well.
A DMARC record set to p=none with a report address will not block mail, but it gives you visibility into which servers are sending as your domain, which is useful while you confirm the SPF fix has actually taken effect everywhere.
Mistakes to avoid while merging
- Adding a second
allmechanism. Only the first one SPF evaluators reach is used, so a second one is pointless at best and confusing at worst; keep exactly one, at the end of the line. - Changing
~allto-allwithout warning anyone. A hard fail is stricter and can cause legitimate mail from a forgotten sending source to be rejected outright, so confirm every sending service is actually included first. - Forgetting subdomains. If a subdomain such as
mail.yourdomain.comsends its own email, it needs its own SPF record; it does not automatically inherit the root domain’s record.
Rather have it fixed for you?
We merge multiple SPF records into one correct line, and check DKIM and DMARC at the same time, for $49 flat, usually the same day. Get it fixed.
Multiple SPF records: quick answers
What happens if I have multiple SPF records and do nothing?
SPF returns a PermError for every message you send from that domain, which most receiving servers treat as a failure. Depending on your DMARC policy, this can mean mail lands in spam or is rejected outright.
Can I just delete one of the multiple SPF records instead of merging?
Only if the record you delete is not actually needed, for example a leftover from a service you no longer use. If both records cover services you actually send mail through, you need to merge them into one, not simply remove one.
How long does it take after I merge multiple SPF records for mail to improve?
The DNS change itself usually takes effect within an hour. Any deliverability reputation damage caused while the records were broken can take a little longer to recover as receiving servers see clean, passing authentication again.
Does merging SPF records affect DKIM or DMARC?
No, SPF, DKIM and DMARC are separate records that work together but do not depend on each other’s syntax. Fixing SPF alone will not break DKIM or DMARC, though it is worth checking all three while you are in your DNS settings.